GalaChain attacker drains $3M using 55-day-old signatures
In brief
- Attacker drained ~2 billion GALA tokens ($3M) from nine wallets using 74 historical signatures from failed transactions.
- GalaChain's EIP-712 verifier accepted type definitions from requests instead of deriving them from operations, enabling signature mismatches.
- 56 of 59 targeted account-token combinations were completely drained on first attempt, suggesting prior reconnaissance.
- Vulnerability persisted through CertiK and Hashlock security audits before Gala patched it.
The Signature Replay Vulnerability
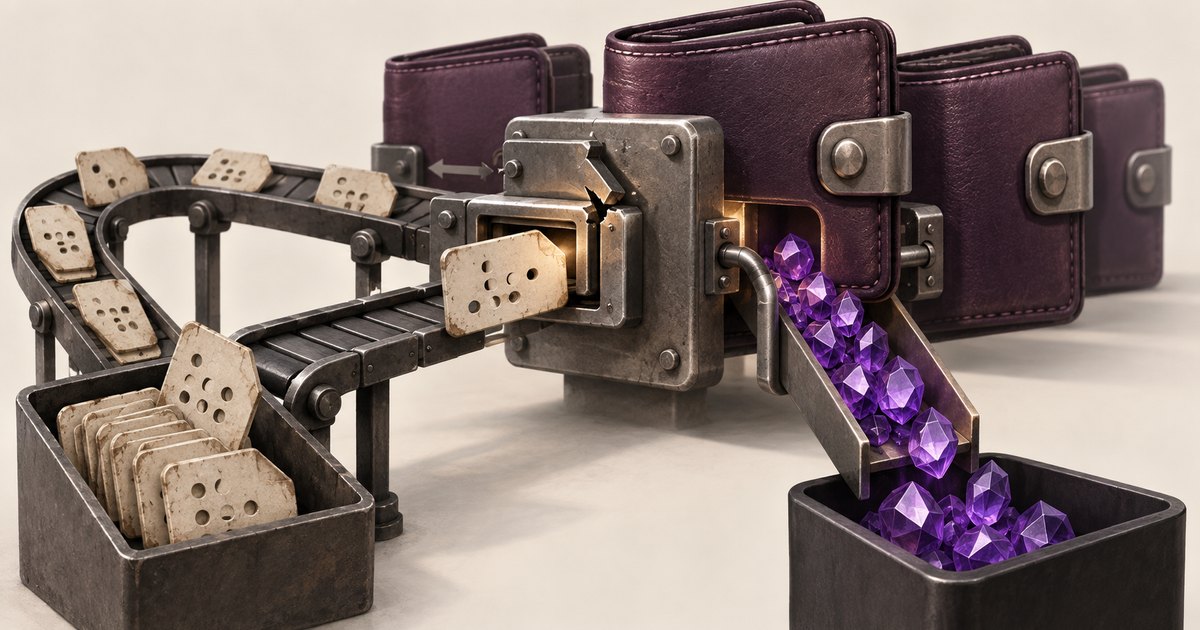
GalaChain's EIP-712 verifier contained a fundamental design flaw. Before the patch, the system accepted type definitions supplied with each request rather than deriving them from the invoked operation. This meant an attacker could submit a TransferToken call while claiming it was an AddLiquidity operation — and the signature verification would treat it as valid.
One on-chain example shows a TransferToken call processing about 1.64 billion GALA even though the EIP-712 structure supplied for verification described an AddLiquidity operation. The attacker didn't forge new signatures. They harvested old ones from the ledger.
How Failed Transactions Became a Master Key
GalaChain assigned unique transaction keys intended to stop the same signed payload from being submitted more than once, but when a transaction failed, the key could roll back. This meant failed transactions left signatures on the ledger that could be reused.
The attacker collected 74 such signatures from failed transactions dating back 55 days. 57 of the 60 historical source transactions linked to the exploit contained at least one failed inner operation, while none completed entirely successfully. By replaying these signatures with manipulated type definitions, the attacker gained access to wallets that had never authorized a transfer.
Precision and Speed
The attack's precision revealed advance planning. Of 59 account-token combinations targeted during the incident, 56 were drained for their exact balance on the first attempt. This pattern suggests reconnaissance occurred before exploitation began rather than account balances being discovered during the attack itself.
The four largest GALA positions were taken in descending order within 18 seconds. GalaChain recorded 1,066 submissions at a median interval of 4.5 seconds, with 73.9% arriving exactly one block apart. The mechanical efficiency of the exploit suggests automated execution.
What the Audits Missed
The vulnerability survived external security reviews including a CertiK authorization-focused engagement in late 2025 and an SDK review by Hashlock in January. Neither firm flagged the type-definition acceptance flaw or the transaction-key rollback mechanism.
Gala patched the flaws after pausing its bridge during the attack. Gala said investigators found no evidence that the affected users' private keys, seed phrases, or passwords were compromised. The attack relied entirely on exploiting the protocol's own verification logic.