Hardware wallet maker Keystone discloses customer data breach, warns of phishing
In brief
- Keystone detected unauthorized access to its official website on October 20, 2026.
- Shopify API review confirmed on October 23 that customer shipping data was taken.
- Recovery phrases, private keys, passwords and payment data weren't exposed, Keystone says.
- Keystone warns scammers may impersonate it by phone, text, email or mail.
What Keystone says was taken
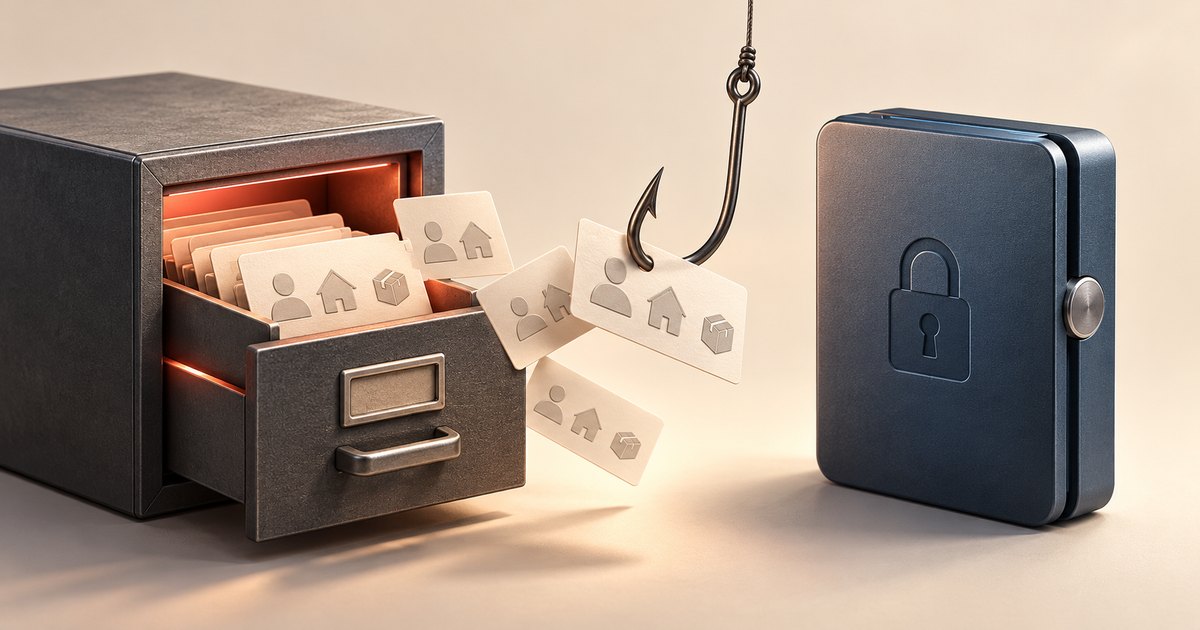
Keystone said that after reviewing API activity with Shopify, it confirmed on October 23 that a third party had obtained customer shipping information. The exposed data included names, contact details, shipping addresses and order details (items and prices).
The list of what wasn't exposed is longer. According to Keystone, payment card and bank details, wallet recovery phrases, private keys and wallet passwords weren't part of it.
Keystone said it blocked the unauthorized access, fixed the vulnerability and launched an investigation. It's emailing affected customers, and the company said a more detailed report would follow.
The impersonation warning
Keystone's own warning focused on scams. The company said scammers might pose as Keystone by phone, text, email or mail, offering refunds, replacement devices or fixes for orders or addresses. Users were told never to share recovery phrases or private keys, never to enter a recovery phrase into a device they didn't order, not to click links in unexpected messages and to trust only official channels.
Keystone said it will never ask for these details.
Why Dogecoin holders are talking about it
The incident isn't tied to any one chain. Keystone's hardware wallet supports DOGE alongside BTC, ETH, SOL and other coins, and the Dogecoin angle came from a community voice rather than from anything specific to the network.
Dogecoin community member Mishaboar warned that affected customers could be targeted with phishing by email, text, phone and possibly physical mail. Mishaboar said mail-based phishing had happened before with Trezor and Ledger customers (a point he raised as precedent, not one Keystone addressed).
"Unfortunately, your home address may now be linked to the fact that you bought a hardware wallet to hold crypto." (Mishaboar, Dogecoin community member)
He urged users not to reveal more about themselves or their families on social media. Mishaboar also repeated the advice Keystone gave: don't share a recovery phrase with anybody, and don't trust unsolicited offers of replacement devices.
That's where the two warnings line up. The data that leaked was shipping data, and according to Keystone the keys themselves stayed out of reach, so the risk both Keystone and Mishaboar flagged is someone using that shipping data to get users to hand over what wasn't taken.
Frequently asked questions
What customer data was exposed in the Keystone breach?
According to Keystone, a third party obtained customer shipping information, including names, contact details, shipping addresses and order details such as items and prices. Keystone confirmed this on October 23, 2026, after reviewing API activity with Shopify.
Were Keystone wallet recovery phrases or private keys leaked?
Keystone said wallet recovery phrases, private keys, wallet passwords, and payment card and bank details were not exposed. The company said it blocked the unauthorized access, fixed the vulnerability and launched an investigation.
How should Keystone customers protect themselves after the breach?
Keystone warned that scammers might impersonate it by phone, text, email or mail, offering refunds, replacement devices or fixes for orders. Users were told never to share recovery phrases or private keys, never to enter a recovery phrase into a device they didn't order, and to trust only official channels.