JPMorgan says vendor cyberattack may have exposed customer names and emails
In brief
- JPMorgan disclosed a cyberattack on third-party service providers Thursday in a post on X.
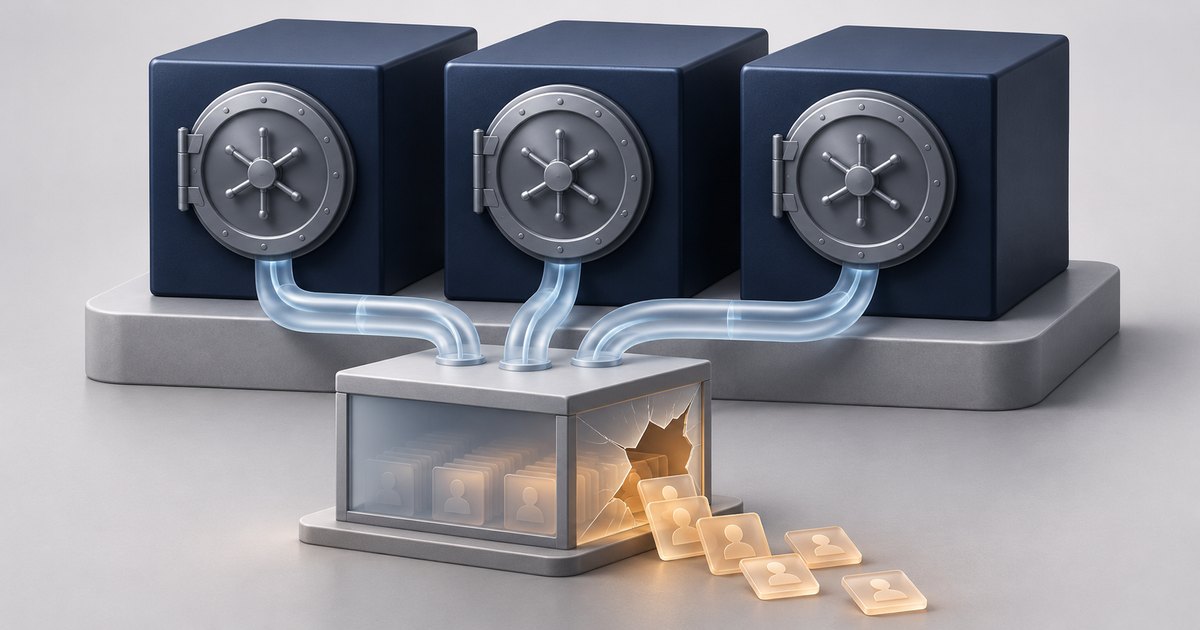
- Customer names and email addresses may have been exposed, the bank said.
- Attackers are believed to have accessed marketing data stored by the vendors.
- JPMorgan will notify affected customers and offer free credit monitoring, the bank said.
- The attack isn't connected to the November 16 Chase outage, JPMorgan said.
What JPMorgan disclosed
The bank said the incident hasn't affected Chase's services. That's the key reassurance for account holders.
JPMorgan said it'll notify customers who may have been affected and provide support such as free credit monitoring, according to Crypto Briefing. The exposure, as the bank described it, involves marketing data held by outside vendors (names and email addresses are the examples it gave), and JPMorgan kept its wording hedged: the data "may have" been exposed, and the attackers are "believed to have" accessed it.
Separate from Monday's outage
JPMorgan also said the cyberattack had no connection to service disruptions some customers reported earlier in the week.
Those disruptions trace back to a technical outage on November 16, when a software bug in the bank's on-premises hardware systems delayed transactions and disrupted online banking and Zelle payments. Thousands of customers reported problems accessing accounts, checking balances and making transfers during the outage (although their funds remained accessible). The bank said that outage wasn't a cyberattack, was limited to Chase and had been resolved by Monday evening.
So there are two incidents in one week. JPMorgan's position is that they aren't related.
A known weak point
Third-party exposure isn't a new problem for the bank. According to Crypto Briefing, a previous incident in 2025 involved SitusAMC, an outside vendor.
The outlet also reported that J.P. Morgan's Chief Information Security Officer warned about third-party vulnerabilities in April 2025. The CISO had repeatedly cautioned that these weak points could affect security standards across the industry, Crypto Briefing said, which puts this week's disclosure squarely inside a risk the bank's own security chief had already flagged in public.
For now, the next step on JPMorgan's side is customer notification. Anyone who gets one can expect the support the bank described, including free credit monitoring.
Frequently asked questions
What customer data may have been exposed in the JPMorgan vendor cyberattack?
JPMorgan said the attack on third-party service providers may have exposed customer information, including names and email addresses. According to the bank, the attackers are believed to have accessed marketing data stored by the vendors. JPMorgan said Chase's services weren't affected.
Is the JPMorgan cyberattack related to the November 16 Chase outage?
JPMorgan said the cyberattack had no connection to the service disruptions customers reported earlier in the week. The bank said the November 16 outage was caused by a software bug in its on-premises hardware systems, wasn't a cyberattack, was limited to Chase and was resolved by Monday evening.
What is JPMorgan doing for customers who may be affected?
The bank said it would notify customers who may have been affected by the vendor cyberattack. It also said it would provide support such as free credit monitoring to those customers.